Is a random password without symbols strong enough? Yes, if it is long enough and every letter is chosen by a secure random generator. Leaving out symbols shrinks the pool of possible characters, but it does not make the result predictable. Length, true randomness, and a unique password for each account matter more.
As of October 30, 2026, current NIST guidance still points the same way: length matters, and character-mix rules do not. You can build a letters-only password with the Secure Password Generator by turning off numbers and symbols, then set a longer length to make up for the smaller pool. Below I explain why that works, where it stops working, and what to do when a website insists on symbols.
Table of Contents
Is a random password without symbols strong enough? What dropping symbols changes
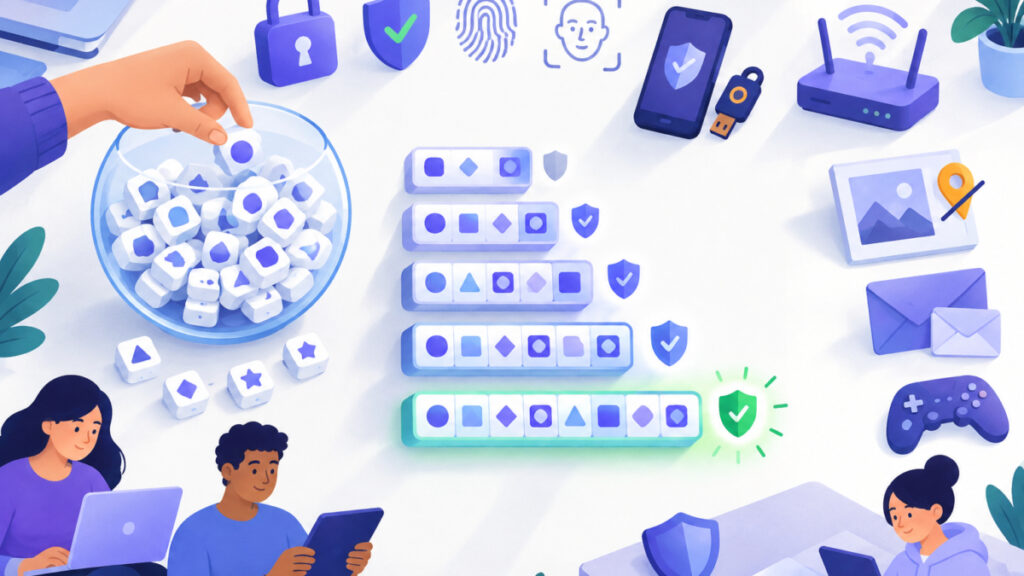
A symbol is simply one more possible character at each position. With lowercase letters only, each position has 26 options. Add uppercase and it has 52. Add digits and symbols and the pool grows further. A bigger pool means more possibilities per character, which is why symbols are so often recommended.
But the pool is only half the story. The other half is how the characters were chosen. Entropy is a measure of unpredictability counted in bits, where each extra bit doubles the number of possibilities. An entropy estimate only applies if every character was picked independently and uniformly at random, the way a cryptographically secure generator does it.
A name, a quotation, a repeated pattern, or a string you typed to look random does not inherit that estimate. Humans are predictable in ways that are hard to notice from the inside.
So a letters-only password is not weak because it lacks symbols. It is weak when it is short, patterned, reused, or already exposed in a breach.
How much do length and alphabet size matter?
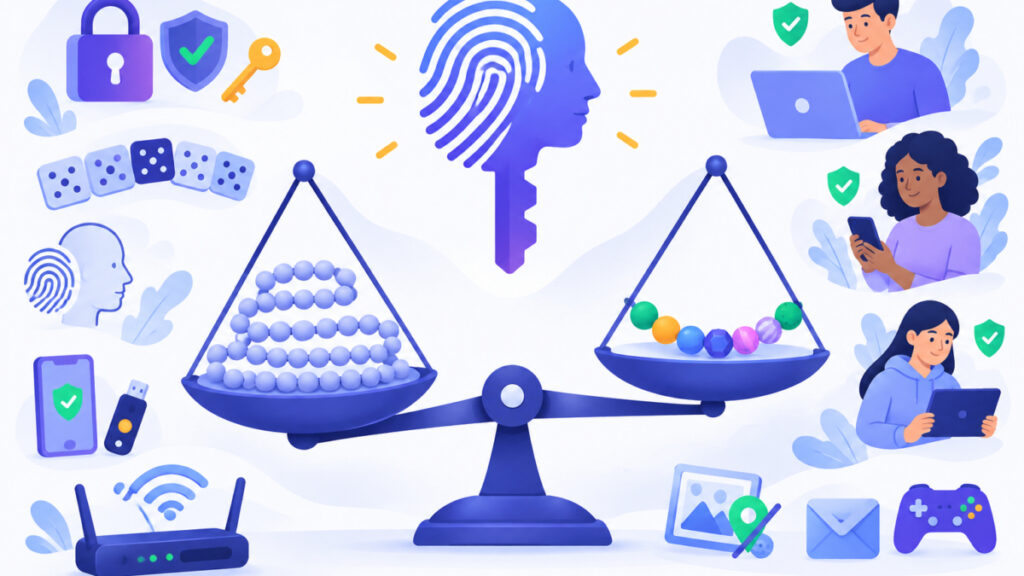
Here is a small calculation, and it comes with a condition: it only holds when each position is chosen independently and uniformly at random. Entropy in bits equals length multiplied by log2 of the pool size.
| Random generation process | Pool size | Theoretical entropy |
|---|---|---|
| 16 lowercase letters | 26 | about 75.2 bits |
| 16 uppercase and lowercase letters | 52 | about 91.2 bits |
| 20 lowercase letters | 26 | about 94.0 bits |
Four extra lowercase letters more than offset the theoretical gain from adding uppercase to a 16-letter password. In other words, adding length is often an easier win than adding character types.
These numbers describe a generation process. They are not a measurement of any password you happen to hold, and they are not a crack-time promise. Real attacks vary a lot: online login pages can rate-limit guesses, while stolen password records depend on how the site stored and hashed them. That is why I avoid universal time-to-crack claims here.
Estimates and scores can also disagree with each other. The article on why a high entropy number can still get a weak score walks through that gap.
Is a random password without symbols strong enough for sites with rules?
It depends on what the site accepts, and it helps to separate official guidance from individual website rules.
What NIST says
NIST SP 800-63B, Revision 4, was released in July 2025. For verifiers, meaning the systems that check your password, it says they must not impose character-composition rules. It requires at least 15 characters when a password is the only authentication factor, and it allows a minimum of eight when the password is only one part of multifactor authentication. It also requires screening proposed passwords against commonly used, expected, or compromised values.
Those are requirements for verifiers. They do not guarantee that every 15-character password is strong, or that every website follows them. NIST’s strength appendix names length as a primary factor, warns that entropy is hard to estimate for human-chosen passwords, and notes that complexity does not stop phishing or keylogging. Phishing means tricking you into typing your password into a fake page. Keylogging means malware recording your keystrokes.
What CISA says
CISA’s password tip sheet recommends at least 16 characters and stresses randomness and uniqueness. Its example of a random string also includes numbers and symbols, so I do not read it as endorsing letters-only strings. It does support the length target.
What if a site demands a symbol?
Follow that site’s rules. Turn symbols back on in the generator and keep the length high. A rule you cannot change is not worth a lockout.
What steps build a strong letters-only password today?
- Open the Secure Password Generator. Keep uppercase and lowercase on and switch numbers and symbols off. The tool uses cryptographically secure random number generation in your browser, according to its page.
- Set the length to 16 or more. Go to 20 or beyond when the site allows it. If you ever need to read the password aloud, the ambiguous-character option helps avoid look-alike letters.
- Generate a fresh password for every account. Do not tweak it by hand afterward, because edits can add patterns.
- Store it in a reputable password manager and paste it in rather than typing it.
- Check for exposure. The Password Leak Checker uses k-anonymity, which means only a short piece of a hash is sent for matching instead of the whole password. Per the tool page, only the first five characters of the SHA-1 hash leave your device. A clean result is not proof that a password has never been exposed.
- Turn on multifactor authentication or passkeys. A passkey is a sign-in method that uses a cryptographic key pair stored on your device instead of a typed password, based on FIDO Alliance and W3C WebAuthn standards.
For a printable version of these habits, the Password Safety Checklist covers ten actions you can take this week.
No length makes up for reuse. A long password shared across two sites is only as safe as the weaker site.
How should you use the Password Entropy Calculator?
For IT and web development beginners
The Password Entropy Calculator shows length, pool size, entropy in bits, total combinations, and an estimated time-to-crack. It works out the pool by looking at which character classes appear in what you type: lowercase adds 26, uppercase adds 26, digits add 10, plus the count of unique symbols. Its page says input is not stored or sent anywhere.
That design has limits worth knowing:
- Observed characters are not the process. A 16-letter password drawn from 52 letters could, by chance, contain no capitals. The calculator would then assume a pool of 26 and understate it.
- A human-made string can look strong. A word with a few swaps may show a large number, though attackers try such patterns first.
- The time estimate uses a fixed guess rate of 10 billion guesses per second. Real attacks may be far slower online or differ widely depending on how passwords are stored, so treat the time as a rough scale, not a prediction.
Use it to explore how length and assumed pool size change the estimate, for example by comparing 16 and 20 lowercase letters. Do not use it as a safety certificate. For pattern checks such as dictionary words and keyboard sequences, the Password Strength Checker looks at different things and pairs well with it.
As a cautious habit, test a sample of the same length and style instead of a password you actually use.
When is a memorable option better than random letters?
Random letters are best for passwords you will store and paste. They are hard to memorize, and that is fine when a password manager holds them.
For something you must type or remember, such as a device unlock or the master password for your manager, words work better. The UK NCSC recommends three random words as one way to build a longer, memorable password (published and reviewed December 21, 2021). Note that random words are a different generation process from independently chosen random letters, so the bit estimates above do not transfer directly.
The Passphrase Generator builds multi-word passphrases, recommends four or more words, and lets you choose the separator. Generate your own and never copy a sample from an article.
Frequently asked questions
Is a lowercase-only random password fine?
It can be, if it is long and generated by a secure random process. Sixteen random lowercase letters have about 75.2 bits of theoretical selection entropy, and 20 have about 94.0 bits. Those figures describe the generation process, not any password you typed yourself.
Is mixed case better than lowercase at the same length?
Yes, at equal length the larger pool gives more possibilities. Sixteen random letters from upper and lower case have about 91.2 bits versus about 75.2 for lowercase only. Adding a few characters to a lowercase password can close that gap.
What if a website requires symbols or numbers?
Follow the site’s rules. Turn those character types back on in the generator and keep the length at 16 or more where the site allows it. NIST says verifiers should not impose composition rules, but individual sites may still do so.
Is a 12-character letters-only password enough?
I would aim higher. NIST SP 800-63B Revision 4 requires at least 15 characters when a password is the only factor, and CISA recommends at least 16. Shorter minimums may be allowed when a password is only one part of multifactor authentication.
Can I make a random-looking password by hand?
I do not recommend it. People tend to fall into patterns without noticing, so a hand-made string does not earn the entropy estimate of a generated one. Use a secure generator and keep the result unedited.
Does a long letters-only password stop phishing?
No. NIST notes that password complexity does not defeat phishing or keylogging. A long password typed into a fake page is still handed over, which is why multifactor authentication and passkeys add real protection.
If the leak checker finds nothing, is my password safe?
Not necessarily. Have I Been Pwned’s Pwned Passwords check uses a five-character hash prefix, and a result absent from that dataset is not proof the password has never been exposed. Keep passwords unique and use multifactor authentication too.
Next steps
So, is a random password without symbols strong enough? Yes, when it is long, generated by a secure random process, and used for one account only. Symbols widen the pool, but length and randomness carry most of the weight. Here is the short recap:
- Generate 16 or more random letters, and go longer when you can.
- Follow a site’s own rules if it requires symbols.
- Use a different password for every account and store them in a reputable password manager.
- Check for breach exposure, and treat entropy estimates as rough guides.
- Turn on multifactor authentication or passkeys.
Related tools and resources on Password Ideas:
- Secure Password Generator
- Password Entropy Calculator
- Password Leak Checker
- Passphrase Generator
- High Password Entropy but Weak Strength Score: Why It Happens
- Password Safety Checklist (PDF)